The Hive Zero Trust Alert to Case Integration
Support Statement
This documentation is provided "as is" without support for 3rd party software. The level of support for this integration guide is best effort without any SLA on response time. No 3rd party product support can be provided by Superna directly. 3rd party components require support contracts. See EULA for more details.
Overview
TheHive is a powerful and versatile tool for security incident response with strong automation capabilities. It has a user-friendly and intuitive interface that makes it easy to create, manage, and analyze security incidents.
Solution Overview
Superna Defender Zero Trust API receives webhook alerts and parses the key data into HTTPS API payload events that are sent to TheHive endpoint URL. TheHive is a modular architecture that provides real-time visibility of your IT infrastructure, which you can use for threat detection and prioritization.
Advanced Zero Trust Capabilities
- Webhook to native HTTPS collector API case creation
- Webhook updates to the same incident search for a pre-existing case and add a comment with the payload from the update
What Is TheHive?
TheHive offers a comprehensive 4-in-1 Security Incident Response Platform, serving as a vital tool for Security Operations Centers (SOCs), Computer Security Incident Response Teams (CSIRTs), Computer Emergency Response Teams (CERTs), and all information security professionals involved in swift and effective handling of security incidents. With its seamless integration with MISP and advanced capabilities for task management, evidence handling, and threat intelligence integration, TheHive is an indispensable tool for modern SOC, CSIRT, and CERT teams.
Integration Architecture
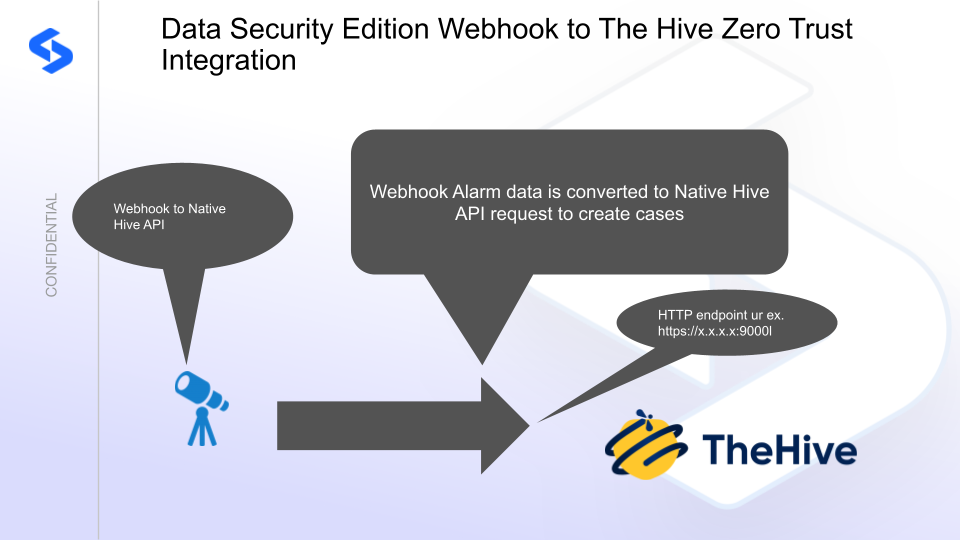
Solution Configuration in TheHive and Data Security Edition Zero Trust
Prerequisites
- Installed Security Edition
- Eyeglass OS appliance version 15.5 — verify with
cat /etc/os-release - License key for the Zero Trust API
- TheHive — download here with an API key that has create case and add comment permissions
Configuration in TheHive
- Log in to the tenant or main console.
- Open the Users section and click on a user account that has organization admin credentials or role.
- Click on the API Key tab of the user account.
- Create an API key and copy the token value for use in the steps below.
Configuration Steps on Eyeglass Virtual Machine
High-Level Steps
- Create the Python location to run the application on the Eyeglass VM.
- Create the Python main application script.
- Create the Linux systemd service and set it to auto-start.
- Create the Zero Trust configuration in Data Security Edition.
- Update the main script to customize it with TheHive Python code.
- Test the script is running as a service.
- Create a test event in Defender to validate alerts appear as indexed parsed events in TheHive.
Configure the Service Start and Python Integration Files
Log in to the Eyeglass VM via SSH as the admin user:
ssh admin@<your-vm-ip>
Become root:
sudo -s

mkdir -p /opt/superna/cgi-bin

chown -R sca:users /opt/superna/cgi-bin

chmod -R u+rwX,g+rwX /opt/superna/cgi-bin
Switch to the SCA user:
sudo -u sca -s

cd /opt/superna/cgi-bin
Create a Python virtual environment for the integration:
python3 -m venv venv-thehive

source venv-thehive/bin/activate
Install required Python packages:
pip install flask requests

deactivate
Create integration script files:
touch thehive.py

touch thehive.sh

chmod +x thehive.py

chmod +x thehive.sh
Create the thehive.sh launch script:
nano /opt/superna/cgi-bin/thehive.sh
Paste the following content into the file:
#!/bin/bash

export PATH="/opt/.pyenv/bin:$PATH"

source /opt/superna/cgi-bin/venv-thehive/bin/activate

exec python /opt/superna/cgi-bin/thehive.py
Make the script executable:
chmod +x /opt/superna/cgi-bin/thehive.sh
Exit back to root:
exit

whoami # confirm you are root
Create the systemd service unit file:
nano /etc/systemd/system/thehive.service
Paste the following content into the file:
[Unit]
Description=Webhook listener for Zero Trust API translations and integrations
After=network.target

[Service]
Type=simple
User=sca
Group=users
WorkingDirectory=/opt/superna/cgi-bin
ExecStart=/bin/bash /opt/superna/cgi-bin/thehive.sh
Restart=always
RestartSec=5

[Install]
WantedBy=multi-user.target
Reload systemd to register the new service:
systemctl daemon-reload
Enable the service to start on boot (do not start it yet):
systemctl enable thehive
Configure Python Packages and Customize the Integration Code
-
Download the Python template code from the link to download (right-click, save as).
-
Open the Python template file in a text editor. Only replace the placeholder values — do not delete any commas.
-
Locate the following section and replace the placeholder values with your TheHive endpoint URL and API key:
# The Hive HTTP Collector Endpoint
THEHIVE_URL = "https://x.x.x.x:9000/api/cases"
THEHIVE_API_KEY = "yyyyyyy" -
Open the production file on the Eyeglass VM:
nano /opt/superna/cgi-bin/thehive.py -
Open the template file locally in Notepad, select all (Ctrl+A), and copy.
-
Paste the clipboard into the SSH terminal session with the open nano editor.
-
Save the file:
- Press Ctrl+X
- Answer Yes to save and exit
-
Start the service and verify it is running:
systemctl start thehive

systemctl status -l thehive
Verify the service returns "active and running". If the service does not start, do not proceed — double-check the steps above.
Configure Defender Zero Trust Webhooks
-
Configure the Zero Trust endpoint in the Ransomware Defender Zero Trust tab.
Recommended ConfigurationSend only Critical and Major events, and only webhooks that set lockout or delayed lockout. The goal is to send findings rather than a list of alarms that do not pinpoint a security incident. Customers can customize based on specific requirements.
-
The endpoint URL uses localhost and sends webhooks to the application service listening on port 5000:
http://localhost:5000/webhook -
Add the following headers to complete the webhook configuration:
- Content-Type:
application/json - content-encoding:
gzip
- Content-Type:
-
Click Save to commit the configuration.
-
Click Save on the main Webhook configuration page.
How to Test the Integration with TheHive
- Get the IP address of the Eyeglass VM.
- Download the curl command template and open it with a text editor. Locate the IP address of Eyeglass at the very end of the text and replace it with the IP address of your Eyeglass VM.
- Copy all the text in the text editor.
- SSH to the Eyeglass VM as the admin user.
- Paste the entire CLI command to the SSH prompt to send sample data to the running Zero Trust application.
A successfully processed webhook test returns the following text in the SSH terminal:
done sending event to The Hive and check for http 200 and success count in response
To review the process logs from the web application:
sudo -s

journalctl -f -u thehive
To log to a file and review with nano, showing only the most recent 250 lines:
journalctl -f -n 250 -u thehive > /tmp/thehive.log

nano /tmp/thehive.log
The response code from TheHive API call should show HTTP 200 status code and successCount 1 to indicate the case was successfully created.
TheHive SecOps Administrators Integration Experience
Once the integration is complete, example cases created by the integration are visible in the TheHive dashboard with full event details from the Zero Trust payload.